Weekday
Nov 16 – Jan 18
- Lancer InfoSec Senior Trainer
- Live Online - Weekend Batch
- 06:00 PM – 08:00 PM IST
₹ 39,999
₹ 60,000
EMI from ₹6,667/month
1
🔥Only10 seatsleft
at Early Bird price
at Early Bird price
Student Training: 90 Hours (45 Days x 2 Hours) Weekdays
Working Professionals: 90 Hours (45 Days x 2 Hours) Weekdays
Intensive Bootcamp: 90 Hours (45 Days x 2 Hours)
This comprehensive course covers Web Application Security, Network Security, Source Code Security, and Android Application Security, helping participants understand real-world security threats and develop the skills required to assess and secure modern IT infrastructures and applications. The training focuses on practical methodologies, industry-standard tools, vulnerability identification, exploitation in authorized lab environments, risk assessment, and professional security reporting. Whether you are starting your cybersecurity journey or looking to advance your penetration testing skills, this course provides a structured learning path to build practical VAPT expertise.
Course Curriculum
Introduction to VAPT
Introduction to web applications and Android applications
Networking fundamentals: IP, ports, TCP/UDP, DNS and HTTP/HTTPS
Linux fundamentals and essential commands
Lab setup and essential tools
Web requests and responses
Introduction to web applications
Using web proxies
Information gathering and reconnaissance
Fuzzing applications
JavaScript deobfuscation
Login brute forcing in authorized labs
Session security
Web services and API attacks
Hacking WordPress
Exploitation and vulnerability validation
OWASP Top 10 Vulnerabilities
Network reconnaissance and information gathering
Port scanning and service enumeration
Network mapping using Nmap, RustScan
Service version detection
Vulnerability scanning
Common network service misconfigurations
SSH, FTP, SMB, DNS and database service security
Exploitation and validation of discovered vulnerabilities
Privilege escalation concepts
Linux Privilege escalation concepts
Windows Privilege escalation concepts
Network hardening and remediation
Android Fundamentals
Android architecture and OS internals
Android security model
Android application structure and APK internals
Lab setup and essential tools
Static Analysis and Reverse Engineering
Static code analysis using JADX and Apktool
Automated analysis using MobSF
APK and AndroidManifest.xml analysis
Insecure permissions and hardcoded secrets
Reverse engineering
Dynamic Analysis and Exploitation
Exploiting exported activities
Exploiting exported services and broadcast receivers
Exploiting deep links and WebViews
Exploiting insecure local data storage
Injection attacks
Hooking with Frida
Bypassing SSL pinning
End-to-end mobile application penetration testing
Introduction to secure code review
Static Application Security Testing (SAST)
Manual source code analysis
Identifying hardcoded credentials and secrets
SQL Injection and command injection in source code
Cross-Site Scripting and input validation flaws
Authentication and authorization weaknesses
Cryptographic failures and insecure data storage
Security misconfigurations and insecure coding practices
Vulnerable dependencies and outdated components
Source code vulnerability validation and remediation
Integrated web, network and mobile security testing
Correlating source-code findings with application vulnerabilities
Vulnerability evidence collection
Risk and severity classification
Professional VAPT report preparation
Remediation recommendations and retesting
Nov 16 – Jan 18
₹ 39,999
₹ 60,000
EMI from ₹6,667/month
Course Details
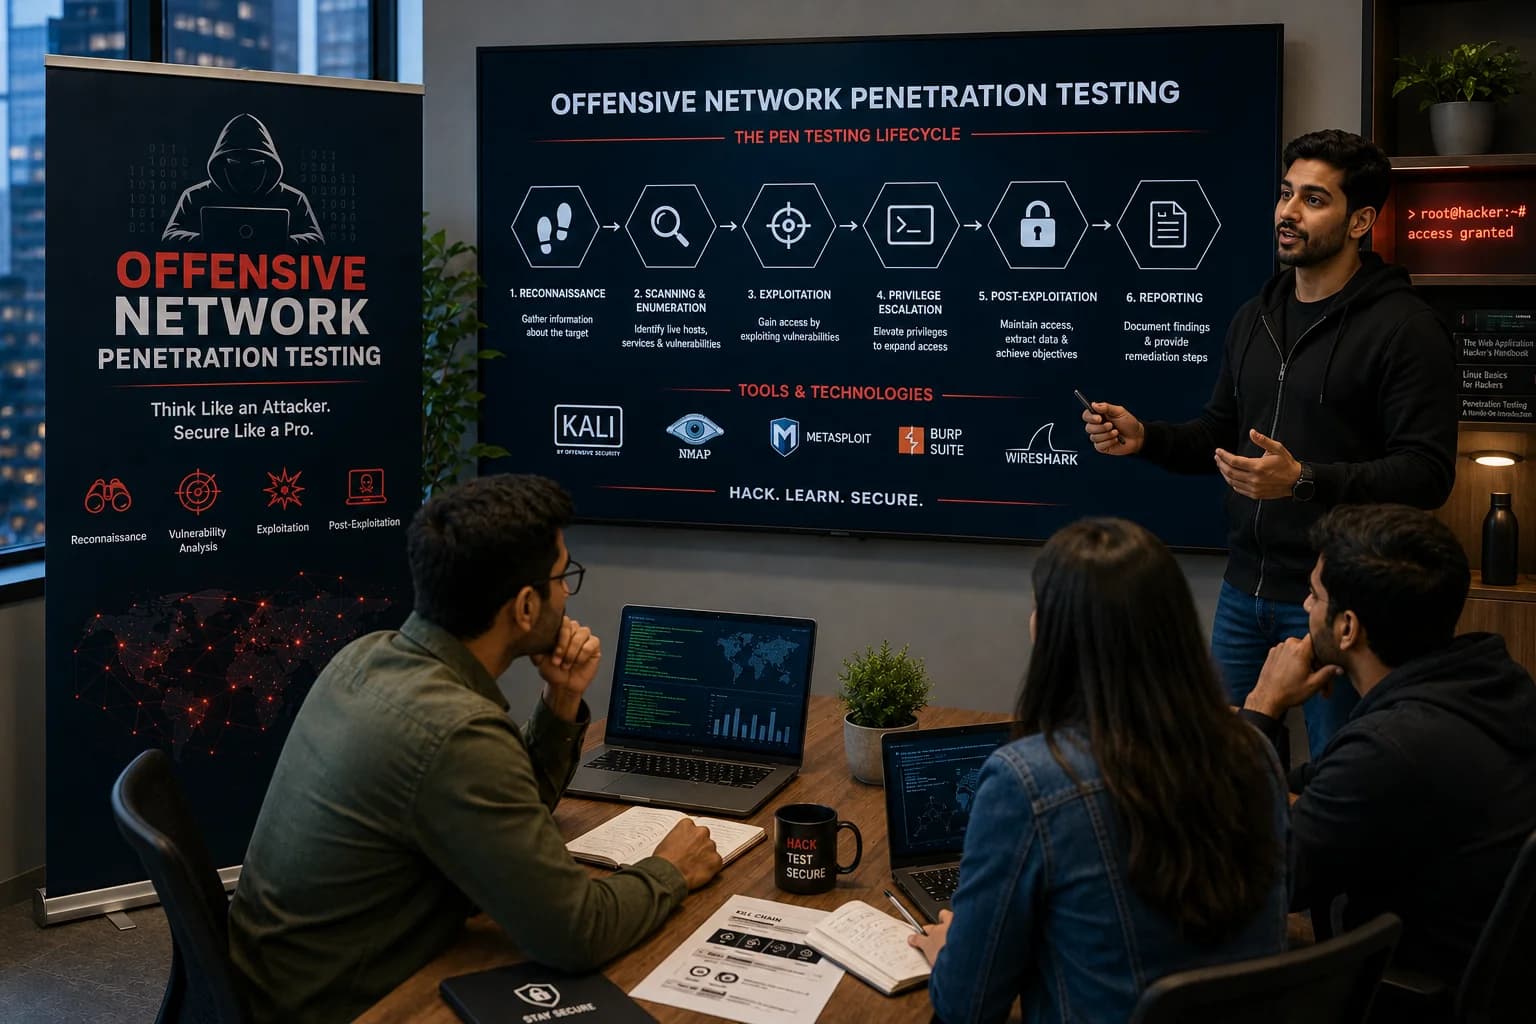
This course is designed to provide participants with the knowledge and practical skills required to perform professional Web, Network, Source code, Android penetration testing engagements. Participants will learn the complete penetration testing lifecycle, including reconnaissance, enumeration, vulnerability assessment, exploitation, privilege escalation, pivoting, web service testing, and reporting using industry-standard tools and methodologies in realistic enterprise environments.
Participants should have a basic understanding of computer networks, TCP/IP, operating systems, and cybersecurity fundamentals. Familiarity with Linux and Windows environments, command-line tools, and basic networking concepts is recommended. Prior penetration testing experience is not mandatory, but a foundational understanding of information security will help participants follow the practical exercises effectively.
Learning Objectives
Understand the complete Assessment & penetration testing lifecycle and professional methodologies. Perform structured vulnerability assessments and penetration tests. Identify security weaknesses in web and mobile applications.
Perform reconnaissance, network discovery, and service enumeration across enterprise environments Assess network infrastructure for potential security vulnerabilities. Conduct source code security reviews.
Conduct vulnerability assessments and validate findings using manual and automated techniques. Understand common attack techniques and security risks. Use industry-standard VAPT tools effectively.
Exploit common network and web service vulnerabilities to obtain initial access in authorized environments. Validate and prioritize identified vulnerabilities. Recommend appropriate remediation measures.
Perform password auditing, privilege escalation, and basic network pivoting techniques. Prepare professional VAPT assessment reports. Follow ethical hacking practices and authorized testing methodologies.
Frequently Asked Questions
VAPT (Vulnerability Assessment and Penetration Testing) training teaches participants how to identify, analyze, validate, and report security vulnerabilities in applications, networks, and IT infrastructure.
The course covers four major domains:
Web Application Penetration Testing
Network Penetration Testing
Source Code Security Assessment
Android Application Penetration Testing
Yes. The course is suitable for freshers, students, IT professionals, and cybersecurity enthusiasts. Basic computer knowledge is sufficient to get started.
Yes. The training includes hands-on practical sessions, guided lab exercises, real-world security scenarios, and practical vulnerability assessment activities.
Participants will gain exposure to industry-standard tools such as Burp Suite, Nmap, Metasploit, MobSF, JADX, Frida, and other security testing tools.
The VAPT training program is designed as a 45-day training program covering Web, Network, Source Code, and Android Security Testing.
Programming knowledge is helpful, especially for source code security assessment, but it is not mandatory to get started.
TAKE THE NEXT STEP
Enroll in Offensive Network Penetration Testing to gain advanced ethical hacking and security assessment skills.
Offical Vulnerability Assessment & Penetration Testing Curriculum
Lancer InfoSec Training Partner
Our VAPT (Vulnerability Assessment and Penetration Testing) Training Program is designed to provide practical knowledge and hands-on experience in identifying, analyzing, validating, and reporting security vulnerabilities across different technology environments.
Duration
45 Days / 90 Hours
Format
Live Online
Learning
Instructor-led
Credential
VAPT Training
4.9/5 learner rating
11,000+ learners worldwide
 Project Management Professional (PMP®) Certification TrainingDisciplined Agile® Leadership (DAL®) Certification TrainingDisciplined Agile® Foundations (DAF®) Certification TrainingProgram Management Professional (PgMP)® Certification TrainingPortfolio Management Professional (PfMP)® Certification TrainingPMI Agile Certified Practitioner (PMI-ACP)® Certification TrainingOffensive Network Penetration TestingAdvanced Web Application Penetration TestingOffensive Android SecurityOffensive Wireless SecurityOffensive API SecurityOffensive Active Directory Penetration TestingOffensive Source Code ReviewOffensive Thick Client Application SecurityVulnerability Assessment & Penetration Testing (Web, Network, Source code, Android) Training


